About one out of every 10 e-commerce websites employ some device to trick people who come to a website, according to studies at Princeton University and the University of Chicago.
 Here are some of the manipulations you may be tricked into using:
Easily signing up for a service, such as an expensive app, but having a difficult time canceling it. You may spend hours searching the site for a solution. These may include devices causing you to feel a sense of urgency if you do not act, such as “offer or coupon expires in twenty minutes.”
Sign up for something free, only to learn you have enrolled in a subscription service. “Free” is emphasized and hidden or disguised is that you need to opt out to avoid being charged.
Making the price of a product hard to find so you compare products.
Being misdirected because the site gets you to focus your attention away from the information it wishes you not to read.
California is the first state to ban such practices under the California Consumer Privacy Act. It’s time for Congress to make such protections national in scope.
Criminals are always looking for new ways to obtain your personal and financial information by pretending to be your bank. If in doubt, don’t transfer money or provide personal information to someone you don’t know via a call, text, email, or pop-up. Ignore requests for remote access. Never grant device access or download apps at the request of unknown companies or individuals.
Scammers Pose as Legitimate Businesses
 Scammers often pose as legitimate businesses. Each year there are more than two million reports of fraud, according to the Federal Trade Commission. And in a November 2021 nationally representative Consumer Reports survey of 2,057 American adults, 95 percent said they had received communication in the previous 30 days that they believed to be fraudulent. Almost half of Americans reported getting six or more phony messages in a typical week. Major types of scams are investment scams, romance scams, and online shopping fraud.
Romance Scams Are Common
Scammers are taking advantage of people looking for romantic relationships online. Most of the people being swindled are older because they are less sophisticated in technology than younger people. Clues to look out for is not being able to actually meet the person. The scammer may say he or she lives abroad or is in the military. They will ask for money – it might be for travel expenses so you can meet. They will use anonymous ways of asking for the money, such as with gift cards, wireless transfers, or cryptocurrency. Dating scams cost Americans over three hundred million dollars each year.
More than 1 in 4 consumers who reported losing money to fraud in 2021 said it started on social media with an ad, post, or email message. More than half of consumers who reported losses to investment scams in 2021 said the fraud started on social media. Measured in dollars lost, about 25 percent of the money stolen in scams was obtained in scams that began on social media.
Amazon impostors are bombarding consumers with millions of robocalls, texts, and emails in hopes of stealing your money. Here is what to watch out for.
New types of Frauds Are Popping Up All the Time
 New types of frauds are popping up all the time on social media. Scammers are always looking for new schemes, and they have come up with one that targets Instagram users. The scam begins with an email warning that your Instagram account will be deleted within 24 hours because you have posted material that violates copyright laws. If you don’t have an Instagram account, you might immediately recognize it for what it is – a scam.
In just nine months of 2021, there were over 2.1 million reports of fraud. The scams are often sophisticated, but you can protect yourself from the most common ones.
The pandemic—and all the time people have been spending online, where scammers can target them by text, email, and social media—has likely led to an increase in scams. International criminal organizations are increasing in number, according to the director of fraud prevention programs at the AARP. “They’ve got offices and employees, and lead lists that they buy off other scammers.”
3 out of 4 American adults have experienced or have been targeted by at least one form of fraud. Here are nine tell-tale signs of a scam. This often happens with Social Security calls, texts, emails, letters, or social media. You can be sure it’s a scam if the caller,
- Threatens to suspend your Social Security number
- Warns you of arrest or other legal action
- Demands or requests immediate payment
- Requires payment by gift card, prepaid debit card, internet currency, or by mailing cash
- Pressures you to disclose personal information
- Requests secrecy
- Threatens to seize your bank account
- Promises to increase your Social Security benefit
- Tries to gain your trust by providing fake “documentation,” false “evidence,” or even the name of a bona fide government official
Here are the kind of things fraudulent callers will say:
“We have to repair your Social Security number.”
“We have to work with the DEA [Drug Enforcement Administration] and the federal criminal process to repair it.”
“We just need to have you move [your money] over here for safekeeping, because otherwise, we might have to arrest you.”
These kinds of “appeals” are phony and you can just hang up on the caller.
Criminals also send out letters that carry bogus SSA logos and the letters contain lies. They may contact you in other ways as their tactics evolve as they use different methods to pretend to be actual Social Security employees.
Gift Cards
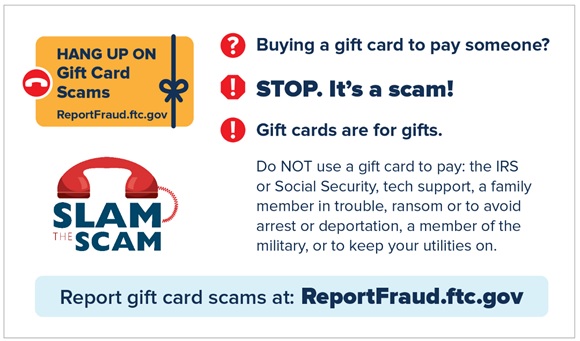 1 in 3 adults are victims of gift card Payment scams. Sweepstakes and advance-fee frauds are among the most common cons. More than a third of U.S. adults have been asked by a scammer to pay a fake financial debt with a gift card, are the findings of an AARP survey . About a quarter of those targeted bought gift cards and shared the numbers with the crooks, losing an average of $200.
Web Scraping
Companies use different tools to collect information and data about you:
- web scraping
- feedback form
- email form to receive newsletters
- form for registration and creation of a personal account
- questionnaire to participate in the loyalty program
- form for filling in contact data to place an order
- registration through social networks
- cookies, Google Analytics, Google Keyword Planner.
Web scraping is an automated process of extracting data from certain site pages according to certain rules using bots. A bot is a program in any programming language whose logic of operation is aimed at retrieving data from websites. The bot’s task is to retrieve web page HTML code that contains information it is interested in. After receiving the code, the scraper analyzes it, extracting all necessary data about you. This way, the bot can open all possible site pages and get information.
 Web scraping can be used to gather any information useful for businesses, whether it’s data about users, products, competitors, and so on. Everything we talked about in data-driven marketing and will talk about below can be obtained through scraping. You have some protection because it is illegal to collect confidential information without permission for sale or to use the material as your own without identifying the source. However, unless you read each website’s “Terms of Use” and copyright information, which can be found on the homepage that tells about how their data can be used and how you can access their site. Scraping also falls under several legal provisions. Illegal scraping is a Violation of the Computer Fraud and Abuse Act (CFAA), and a possible violation of the Digital Millennium Copyright Act (DMCA).
Social Media Safety Tips
The agency urges consumers to report fraud at ReportFraud.ftc.gov and to try to stay safe using these tips. No matter how sophisticated scammers are, there’s plenty you can do to help protect yourself.
- Be sure to call to verify any email or other request for money using a number from a trusted source.Be wary of unsolicited emails or texts prompting you to click a link, provide personal information, or phone calls demanding immediate payment.
- Learn more about different types of phishing and what to look out for.
Limit who can see your posts and information on social media. All platforms collect information about you from your activities on social media, so check your privacy settings to establish restrictions.
- Check if you can opt out of targeted advertising, which some platforms allow.
- If you get a message from a friend about an opportunity — or an urgent need for money — call them. Their account may have been hacked.
- Be wary if you are asked to send funds using cryptocurrency, gift cards, or a wire transfer since that’s how scammers ask people to pay them.
- Never click on suspicious links. Also, check the address bar for the URL of the Web page.
- If someone appears on social media and rushes you to start a friendship or romance, slow down. Beware of romance scams. Never send money to someone you haven’t met in person.
- Before you buy something, check out the company. Search its name online and include words such as “scam” or “complaint.”
Something you can do to help others is to tell others. “Word of mouth” is a powerful prevention tool.


